




Bitcoin Core Changes Security Policy as AI Makes Hidden Bugs Easier to Find

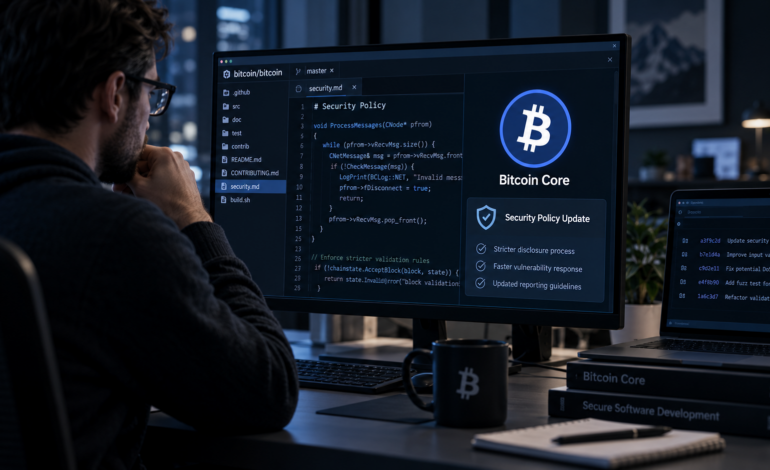
Bitcoin Core, the software used by many computers operating the Bitcoin network, has changed how it handles security vulnerabilities as artificial intelligence makes certain software weaknesses easier to discover.
The new policy, approved on October 22, 2026, introduces faster security updates for vulnerabilities that can be identified with minimal effort, including those that an AI chatbot could rediscover through a simple prompt. The change follows a rise in AI-assisted security research across Bitcoin-related software.
Previously, developers could keep details of certain vulnerabilities confidential for months, sometimes more than a year, to give node operators time to install security updates. However, developers now argue that prolonged secrecy offers limited protection when AI tools can independently identify the same weaknesses.
Why Is Bitcoin Core Changing Its Security Policy?
Bitcoin Core is open-source software that allows computers, known as nodes, to validate Bitcoin transactions and enforce the network’s rules.
Like other complex software, Bitcoin Core can contain programming errors that may create security risks.
Traditionally, when developers discovered vulnerabilities, they assessed their severity and followed a disclosure schedule intended to limit the risk of exploitation. This often involved withholding detailed information until affected software versions were no longer supported. But artificial intelligence is changing that calculation.
Bitcoin Core developer Antoine Poinsot explained that large language models, or LLMs, have made it significantly easier for researchers to identify certain classes of vulnerabilities and recognise previously concealed security fixes.
As a result, keeping information confidential for extended periods may no longer prevent attackers from independently finding the same bugs.
The Bitcoin Core security policy now includes special treatment for easily discoverable vulnerabilities.
How Will the New Security Rules Work?
Under the revised policy, developers can classify a vulnerability as easily discoverable if it can be identified with relatively little effort.
That could include flaws found using simple AI prompts.
Once identified, these vulnerabilities will receive:
- Faster security patches: Fixes will be developed and released as quickly as practical.
- Support for maintained versions: Developers will apply fixes to all actively maintained major Bitcoin Core versions where necessary.
- Earlier public disclosure: Security advisories will be published alongside the patched releases rather than waiting through the usual extended embargo.
- Clearer guidance: Node operators will receive information about the vulnerabilities and available updates.
Other vulnerabilities will continue to follow the existing severity-based disclosure schedules. Critical vulnerabilities that could threaten Bitcoin’s fundamental security will still require special handling. The change does not mean every newly discovered bug will immediately become public.
AI Researchers Flag Thousands of Potential Bitcoin Software Issues
The policy update follows a period of increased AI-assisted cybersecurity research.
In July and August 2026, a volunteer group called the Bitcoin Red Team used AI tools to examine hundreds of Bitcoin-related software projects. According to Cointelegraph, the researchers reported approximately 4,962 potential vulnerabilities across 390 projects. The findings included 85 issues initially classified as critical. However, these were automated research findings, not 4,962 independently confirmed exploitable vulnerabilities. Only a portion had been reproduced or validated when the results were reported.
The research also covered the wider Bitcoin software ecosystem, rather than identifying thousands of confirmed vulnerabilities specifically in Bitcoin Core.
Separately, Core Lightning developers urged some node operators to update their software after receiving credible AI-assisted vulnerability reports.
These developments highlight how AI is increasing both the speed and volume of security research.
Does This Mean Bitcoin Has Been Hacked?
No.
The new Bitcoin Core disclosure policy does not mean Bitcoin’s underlying cryptography has been broken or its blockchain compromised.
Bitcoin’s security relies on several components, including cryptography, network consensus rules and the software used by node operators.
A vulnerability in node software could potentially disrupt individual systems or expose users to certain attacks without compromising Bitcoin’s entire network.
The policy change is intended to make it easier to deliver security fixes before weaknesses can be widely exploited.
As of the October 23 announcement, developers had not identified a specific new exploit under the newly introduced disclosure category.
Could Faster Security Updates Create New Risks?
Although faster patching may help protect users, developers acknowledge that the approach involves trade-offs.
Security updates released quickly may receive less testing than fixes included in major software releases after extended development periods.
This could increase the risk of unintended software problems.
During discussions about the proposal, some developers argued for retaining more flexibility over when vulnerability details should be disclosed.
However, the adopted approach prioritises faster availability of patches when keeping a vulnerability secret is unlikely to stop others from discovering it.
The success of the new policy will depend on how effectively developers test, distribute and communicate future security updates.
Frequently Asked Questions
Has Bitcoin Core been hacked?
No. The October 2026 announcement concerns a change in vulnerability disclosure procedures, not a confirmed compromise of Bitcoin’s underlying network.
Why is Bitcoin Core changing its security policy?
Developers say AI tools have made certain software vulnerabilities easier to discover, reducing the benefits of keeping those flaws confidential for long periods.
What happens when developers find an easily discoverable vulnerability?
They will aim to release security fixes across maintained Bitcoin Core versions as quickly as possible, together with a public security advisory.
Did AI discover nearly 5,000 vulnerabilities in Bitcoin Core?
No. A volunteer research group flagged approximately 4,962 potential issues across 390 Bitcoin-related projects. Many findings had not been independently validated, and they were not all Bitcoin Core vulnerabilities.
Does the change affect Bitcoin wallets?
It primarily concerns Bitcoin Core software and node operators. Wallet users should continue following their wallet providers’ official security guidance.
Should Bitcoin node operators update their software?
Node operators should use maintained Bitcoin Core versions and follow official security announcements, installing relevant updates after reviewing the release guidance.