




Scammer Gets Scammed: $4.8 Million in Bitcoin Stolen Through Compromised Ledger Wallets

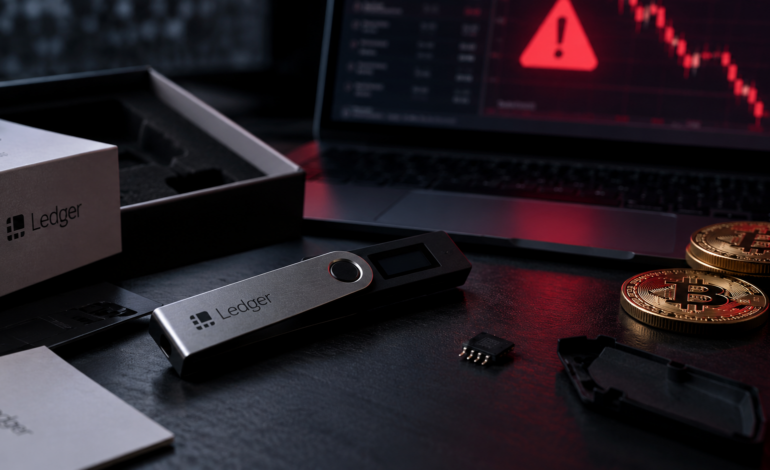
In a rather unusual twist in the cryptocurrency world, a suspected online scammer has reportedly lost 60 Bitcoin (BTC), worth approximately $4.8 million, after unknowingly storing the funds on compromised Ledger hardware wallets.
The individual, who allegedly made money by tricking people through fake online jobs, became a victim of another group of cryptocurrency thieves.
Blockchain analytics firm Chainalysis identified the loss as part of a much larger operation involving tampered Ledger devices distributed across Southeast Asia.
The incident is a reminder that even scammers are not immune to cryptocurrency theft. Apparently, being good at stealing crypto does not guarantee being good at keeping it.
How Did the Scammer Lose $4.8 Million?
The individual reportedly purchased three Ledger hardware wallets that had secretly been modified with malicious components.
Ledger wallets are physical devices designed to store cryptocurrency private keys offline, protecting users from many forms of online hacking.
However, these particular devices had been tampered with before reaching their users.
The compromised devices contained hidden components capable of capturing wallet recovery phrases.
When the scammer set up the wallets, the malicious hardware reportedly exposed the information needed to access the cryptocurrency.
The attackers subsequently drained all three wallets, stealing approximately 60 BTC and transferring the funds to the same destination wallet.
The scammer’s identity has not been publicly established in the reports.
The Scammer Was Running a Fake Online Job Scheme
The story becomes even more interesting when considering how the stolen Bitcoin was reportedly obtained.
Chainalysis linked the individual to a task scam, a form of online fraud that targets people searching for opportunities to earn money.
Victims are offered seemingly simple jobs, such as completing online tasks, promoting products or posting reviews.
Initially, participants may receive small payments to convince them that the opportunity is legitimate.
Eventually, however, they are told their accounts have developed negative balances or that they must deposit additional money to unlock their earnings.
Instead of receiving payment, victims lose their own funds.
In this case, the suspected operator of such a scheme reportedly became a victim of another criminal operation.
Ledger Confirms Hardware Wallet Tampering Attack
The incident forms part of a broader attack involving compromised Ledger devices distributed through third-party resellers.
In an official security statement updated October 15, Ledger confirmed that criminals purchased genuine hardware wallets, opened them and installed hidden electronic components.
The devices were then returned to reseller distribution channels.
The malicious components were designed to capture users’ recovery phrases during wallet setup, allowing attackers to access their funds.
Ledger maintains that the attack did not compromise its core technology.
The company stated that its secure chips, operating systems and servers had not been breached. Instead, criminals physically modified devices after they had left Ledger’s control.
Ledger also instructed authorised resellers and distributors in Southeast Asia and Hong Kong to suspend sales while investigations continued.
Frequently Asked Questions
Did Ledger itself get hacked?
According to Ledger, its secure chips, operating systems and servers were not compromised. The attack involved criminals physically modifying genuine devices after they left the company’s control.
How much Bitcoin did the scammer lose?
The suspected scammer reportedly lost approximately 60 BTC, valued at around $4.8 million at the time of reporting.
Are all Ledger wallets unsafe?
No. The confirmed attack involved particular devices tampered with through reseller distribution channels. Ledger has not reported a general compromise of all its hardware wallets.
Can a hardware wallet be hacked without internet access?
Yes, physical tampering and compromised recovery phrases can expose funds even when private keys are normally stored offline. Hardware wallets significantly reduce certain risks but do not eliminate every possible attack.